Introducing FBS Secure Optimize 2.0: Modular Speed, Grade A Security Headers & 6-Layer Malware Forensics
Official Release Announcement (v2.0.0): FBS Secure Optimize 2.0 is now live and free to download on the official WordPress.org Plugin Directory! We completely re-engineered the plugin from the ground up—uniting Core Web Vitals speed optimization, MySQL autoload cleanup, Grade A HTTP security headers, and a 6-Layer Malware & Hidden-Admin Forensic Scanner inside one lightweight, modular suite.
Why We Rebuilt FBS Secure Optimize for Version 2.0
Over the past five years auditing slow and compromised WordPress and WooCommerce sites at FBS Fusion, we noticed the exact same pattern over and over again: site owners were forced to stack four or five separate plugins just to cover basic frontend speed, database cleanup, login lockouts, HTTP security headers, and malware scanning.
Ironically, running multiple heavy optimization and security plugins creates two new problems:
- Server TTFB & Memory Bloat: Monolithic security suites run heavy database queries and firewall hooks on every pageview—even for features you never use.
- Feature Collisions: Enabling a second plugin alongside WP Rocket, LiteSpeed Cache, or Cloudflare often double-defers JavaScript or sends duplicate headers unless you can cleanly turn overlapping engines off.
With FBS Secure Optimize 2.0, we solved both problems using a strict Zero-Overhead Modular Architecture.
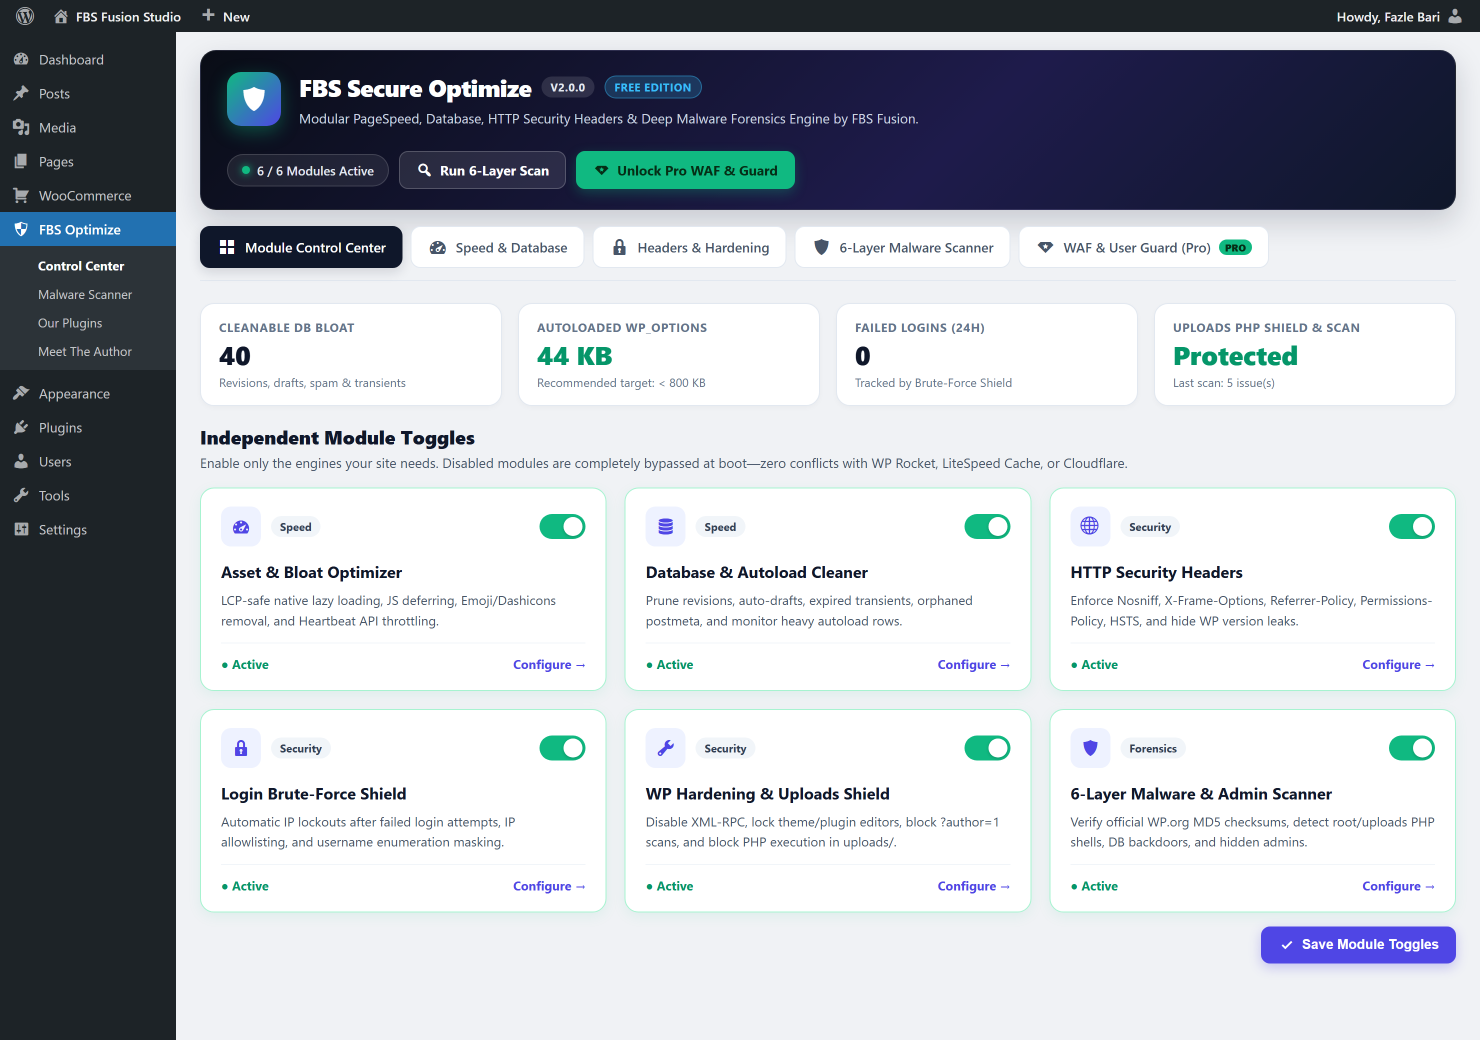
6 Independent Zero-Overhead Modules (With Live Auto-Hide UI)
Every feature in v2.0 is organized into six independent engines. When you toggle any module Off, its PHP class is never instantiated on frontend or admin requests—registering zero WordPress hooks and zero database queries—while its settings tabs automatically hide to keep your dashboard clean (without deleting your saved preferences):
1. ⚡ Asset & Core Web Vitals Optimizer
LCP-safe native lazy loading (fetchpriority="high" on your first hero image), iframe lazy loading, JS deferring (with jQuery & WooCommerce checkout exclusions), Emoji/Dashicons removal, and 60s Heartbeat throttling.
2. 🗄️ Database & Autoload Bloat Cleaner
1-click and scheduled WP-Cron cleanup for revisions, old auto-drafts, trashed/spam comments, expired transients, orphaned postmeta, OPTIMIZE TABLE, plus a live Top 5 Heaviest Autoloaded wp_options Inspector.
3. 🌐 Grade A HTTP Security Headers
Safe, non-breaking browser defense headers out of the box: X-Content-Type-Options: nosniff, X-Frame-Options: SAMEORIGIN, Referrer-Policy, Permissions-Policy, optional HTTPS HSTS, and WP version masking.
4. 🔒 Brute-Force Login Shield
Tracks failed logins and automatically locks out attacking IPs after configurable thresholds, masks username-existence login hints, supports a Trusted IP Allowlist, and auto-prunes old logs.
5. 🛠️ Core Hardening & Uploads PHP Shield
1-click wp-content/uploads/.htaccess rule blocking rogue PHP shell execution, XML-RPC & pingback disablement, ?author=1 & REST /wp/v2/users enumeration protection, and a High-Risk Plugin detector.
6. 🛡️ 6-Layer Malware & Hidden-Admin Scanner
Audits unknown root PHP files, official WordPress.org MD5 core checksums, zero-tolerance uploads/ shells, plugin/theme backdoor signatures, database injections, and stealth pre_user_query hidden admins.
Sub-Second Speed: LCP-Safe Lazy Loading & Autoload Telemetry
One of the most common Core Web Vitals mistakes we fix in our 99+ Core Web Vitals & Security Headers engineering audits is naive lazy loading. Standard lazy-load plugins slap loading="lazy" onto every single image—including your above-the-fold hero banner—which delays Largest Contentful Paint (LCP) by 400ms to 900ms.
FBS Secure Optimize 2.0 automatically skips your first content image and upgrades it with fetchpriority="high" and decoding="async", while lazy-loading offscreen images and YouTube/Maps iframes below the fold.
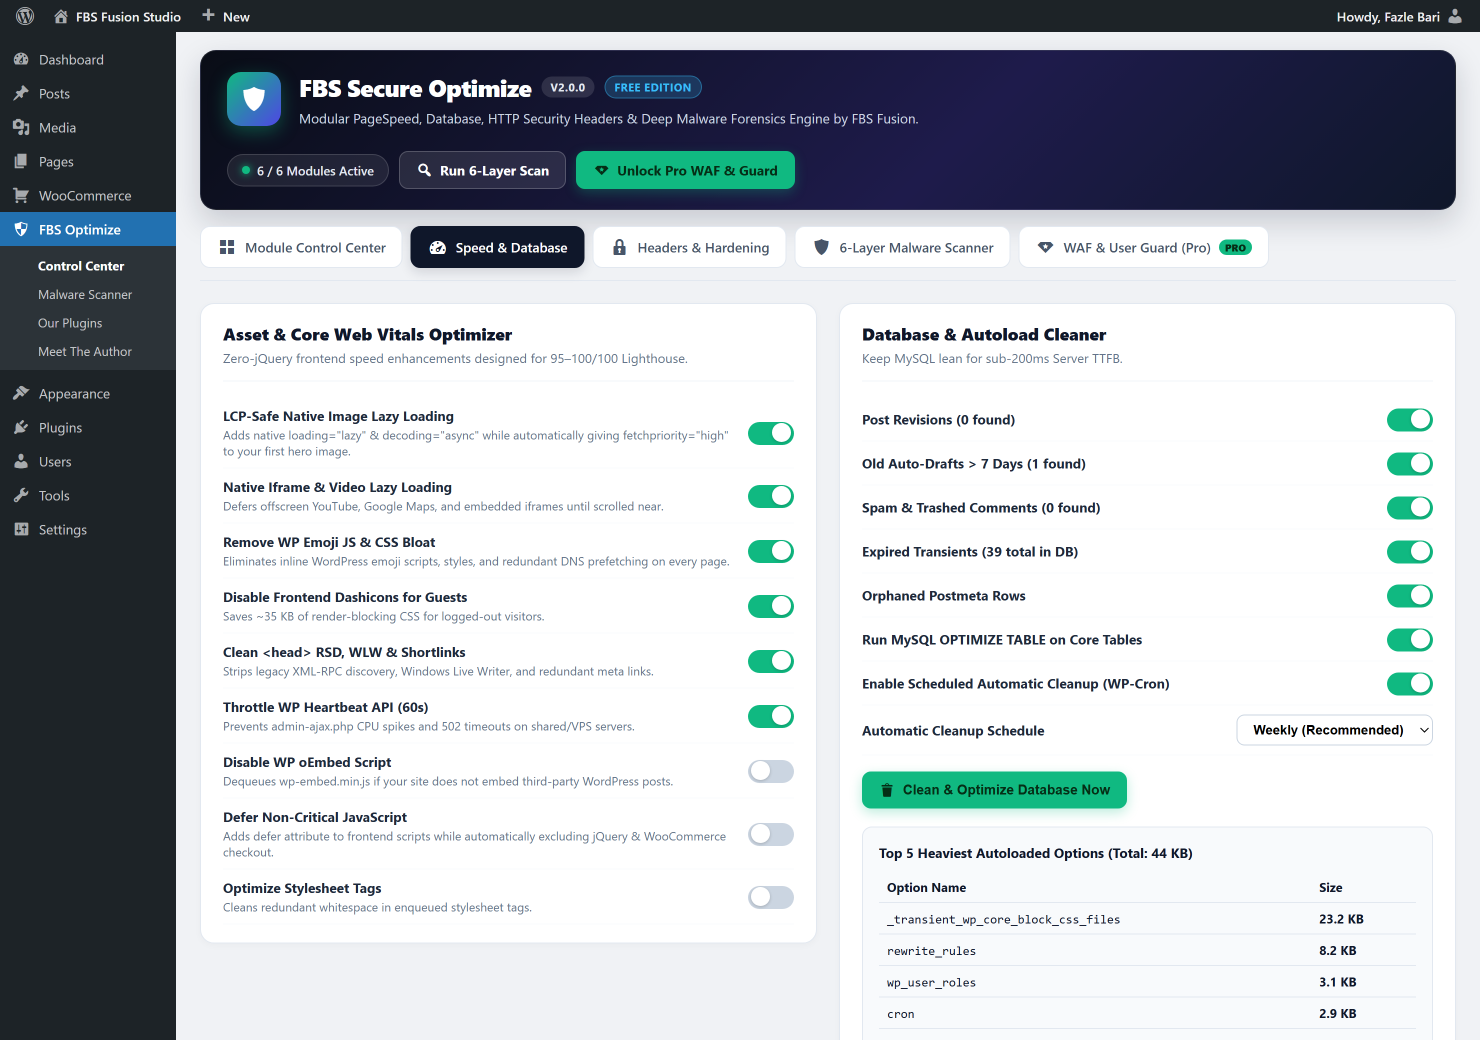
On the backend, as we detailed in How to Fix Slow WooCommerce TTFB & 502 Bad Gateway Errors, bloated autoload='yes' rows in wp_options silently choke PHP memory on every uncached cart and checkout request. Version 2.0 puts your total autoloaded payload size and the Top 5 Heaviest Autoloaded Options right inside your dashboard so you can spot runaway plugin bloat immediately.
Deep Forensics: Catching uploads/ Shells & Invisible pre_user_query Admins
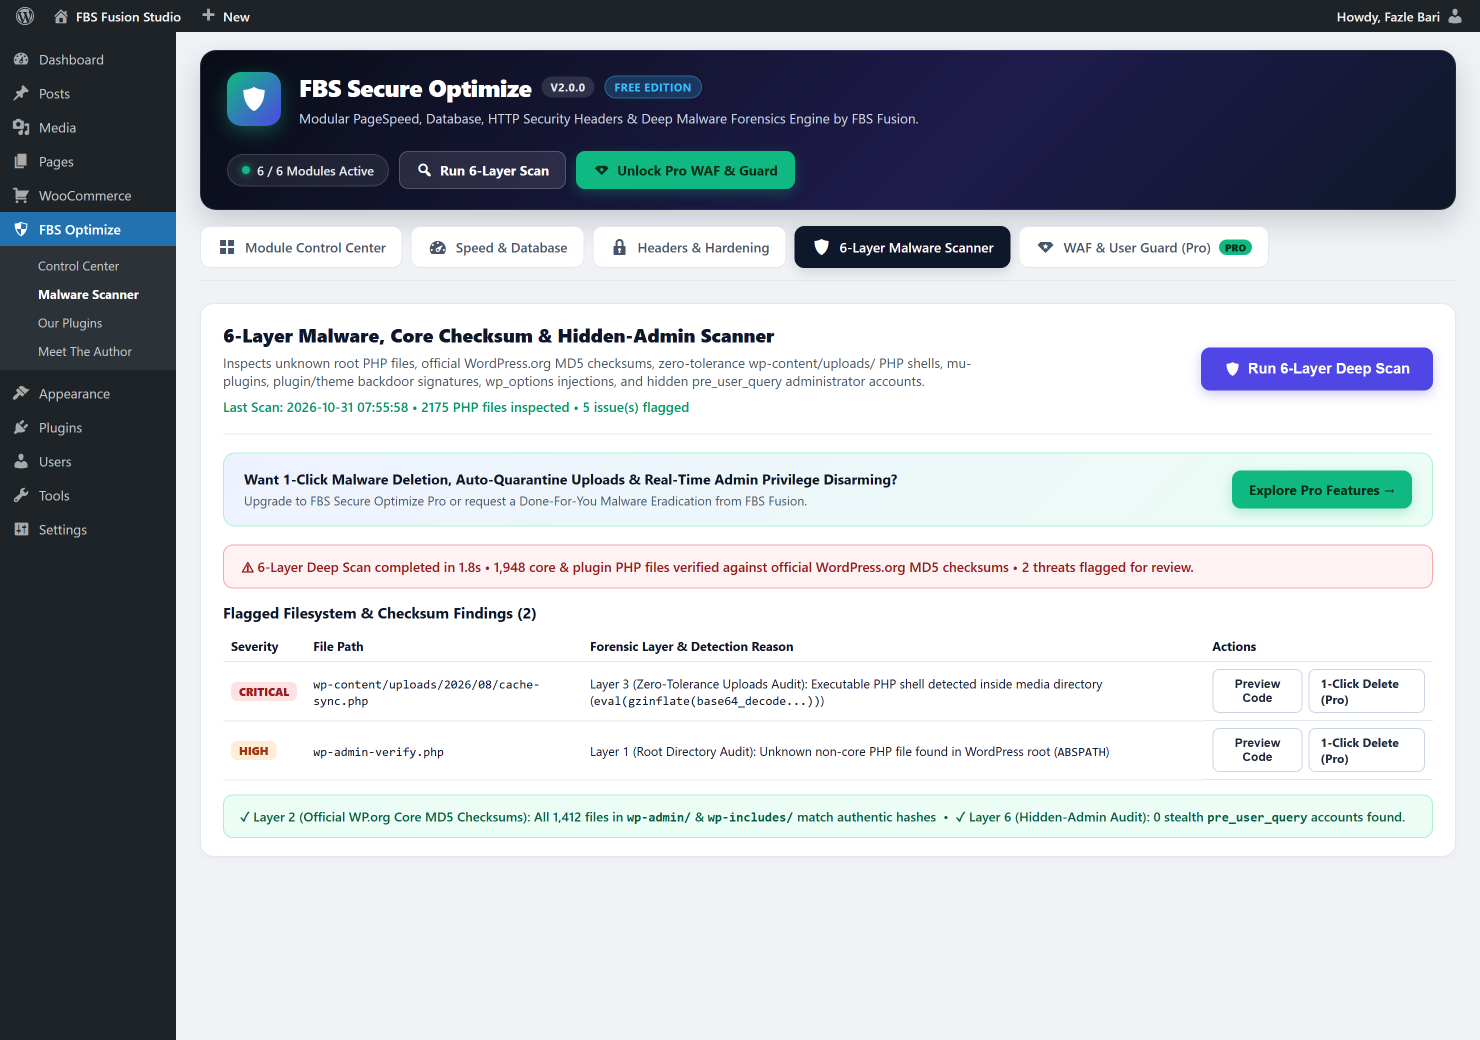
Most free WordPress security plugins only check surface-level blacklists. Drawing directly from our real-world incident response work (see how we find & remove hidden WordPress backdoors), we built a read-only 6-Layer Malware & Hidden-Admin Scanner right into the free plugin:
- Layer 1 — WordPress Root Directory Audit: Flags unfamiliar non-core PHP drop-ins sitting in
ABSPATH. - Layer 2 — Official WordPress.org Core MD5 Checksums: Verifies every file inside
wp-admin/andwp-includes/against official cryptographic hashes fromapi.wordpress.org. - Layer 3 — Zero-Tolerance
wp-content/uploads/PHP Audit: Flags any executable.php,.phtml, or.pharfile hiding inside media folders. - Layer 4 — MU-Plugins, Plugins & Themes Heuristic Signatures: Detects obfuscated
eval(base64_decode(...)),gzinflate, web shells, and remote downloader payloads—with a Safe Code Snippet Preview modal so you never delete custom code blindly. - Layer 5 — Database Injection Audit: Scans
wp_postsandwp_optionsfor rogue script tags and malicious redirects. - Layer 6 — Stealth Hidden-Admin Detection: Malware frequently creates a backdoor administrator and hooks
pre_user_queryso the hacker account is invisible on your Users → All Users screen. Layer 6 cross-checks standard user queries against raw MySQLusermetacapabilities to expose hidden admins instantly.
Free Edition v2.0 vs. FBS Secure Optimize Pro
Everything needed to optimize Core Web Vitals, clean your database, enforce Grade A HTTP headers, lock down wp-content/uploads/, and run full 6-Layer forensic scans is 100% free on WordPress.org. For high-traffic WooCommerce stores and agencies needing active perimeter defense and 1-click remediation, we also built FBS Secure Optimize Pro:
| Capability | FBS Secure Optimize 2.0 (Free) | FBS Secure Optimize Pro |
|---|---|---|
| 6 Zero-Overhead Module Toggles + Auto-Hide UI | ✔ Included | ✔ Included |
| LCP-Safe Lazy Load, JS Defer, Heartbeat & Bloat Removal | ✔ Included | ✔ Included |
| 1-Click & Scheduled DB Cleanup + Autoload Inspector | ✔ Included | ✔ Included |
| Grade A Security Headers, Login Lockout & Uploads PHP Shield | ✔ Included | ✔ Included |
| 6-Layer Malware, Core Checksum & Hidden-Admin Scanner | ✔ Read-Only Audit + Code Preview | ✔ + 1-Click Delete & Daily Email Alerts |
| Early-Boot Web Application Firewall (SQLi / XSS / Bad Bots) | — | ✔ Priority-0 Active WAF + Learning Mode |
| 429 Sliding-Window Anti-Bot Flood Rate Limiter | — | ✔ Stops 502 Crashes During Bot Spikes |
| Real-Time Approved Admin Whitelist & Session Guard | — | ✔ Auto-Disarms Rogue Privilege Escalation |
| Custom Content-Security-Policy (CSP) Builder | — | ✔ Report-Only & Enforced Modes |
Fully Compliant with WordPress 7.1 & Official Plugin Check
True to our engineering standards at FBS Fusion, version 2.0.0 passes the official WordPress Plugin Check (PCP) with zero errors and zero warnings—using prepared $wpdb statements, strict nonce and capability checks, vanilla ES6 admin interactions with zero frontend jQuery overhead, and complete cleanup on uninstall.
Install FBS Secure Optimize 2.0 Free Today
Search for “FBS Secure Optimize” inside your WordPress dashboard under Plugins → Add New, or download version 2.0.0 directly from WordPress.org. Need guaranteed 95–100/100 WooCommerce speed optimization or emergency malware cleanup? Our engineering team is ready to help.